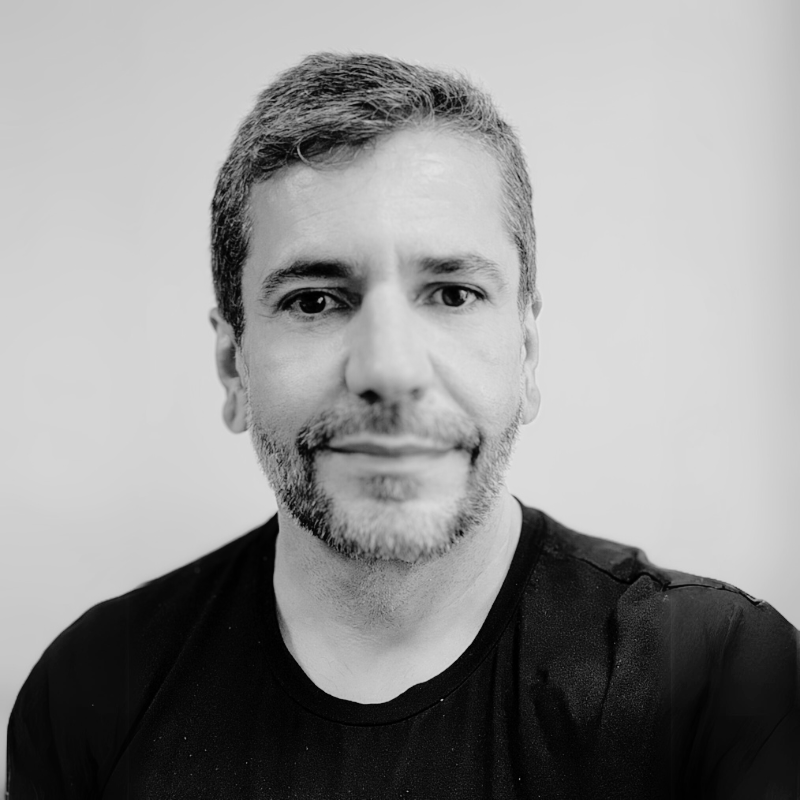
Short (~30 words)Caption, source credit
Ricardo Esper is a CISO and cybersecurity expert with over 35 years of experience. He founded NESS in 1991 and is CISO of IONIC Health and founder of forense.io.
Everything a journalist needs to quote Ricardo Esper without having to ask: ready-to-publish bios, verifiable facts, interview topics and photos. Response within 24 hours.
Ricardo Esper is a CISO and cybersecurity expert with over 35 years of experience. He founded NESS in 1991 and is CISO of IONIC Health and founder of forense.io.
Ricardo Esper is a CISO and international consultant in cybersecurity, digital forensics and privacy, with over 35 years of experience. He founded NESS in 1991, is CISO of IONIC Health and founder of forense.io, Trustness and Infinity Safe. He works with a focus on LGPD, GDPR, HIPAA and SOC 2, as well as corporate counter-espionage (TSCM) and executive protection. He is an ISO/IEC 27001 and 27701 Lead Auditor, and CCISO and CEHv8 certified.
Ricardo Esper is a Chief Information Security Officer (CISO) and international consultant with over 35 years dedicated to information security. He founded NESS in 1991, when cybersecurity was still a niche subject in Brazil, and has since built a portfolio of companies addressing different layers of the problem: forense.io (digital forensics), Trustness (privacy and compliance) and Infinity Safe (executive protection). He is currently CISO of IONIC Health, where he leads security strategy in digital health — a sector under simultaneous pressure from LGPD, HIPAA and ransomware attacks. His work combines governance — ISO/IEC 27001 and 27701 Lead Auditor, and CCISO — with hands-on technical practice (CEHv8, OSINT, TSCM). He is a member of OWASP, IAPP, HackerOne, ERII and OAB/SP, and writes regularly about threats, privacy and incident response at ricardoesper.com.br.
What Brazil's data protection authority can and cannot do, how fines are calculated, and why the 2-business-day notification rule reshapes incident response.
Why hospitals are a preferred target, what changes when the data is clinical, and where ransom payment fails in practice.
Chain of custody, hash integrity, and the collection mistakes that sink an expert report before the hearing.
Bugging, insider exfiltration and executive protection — what is genuine risk and what is industry folklore.
Where corporate data actually leaks in AI usage, and how to write a policy people can realistically follow.